Automated analysis
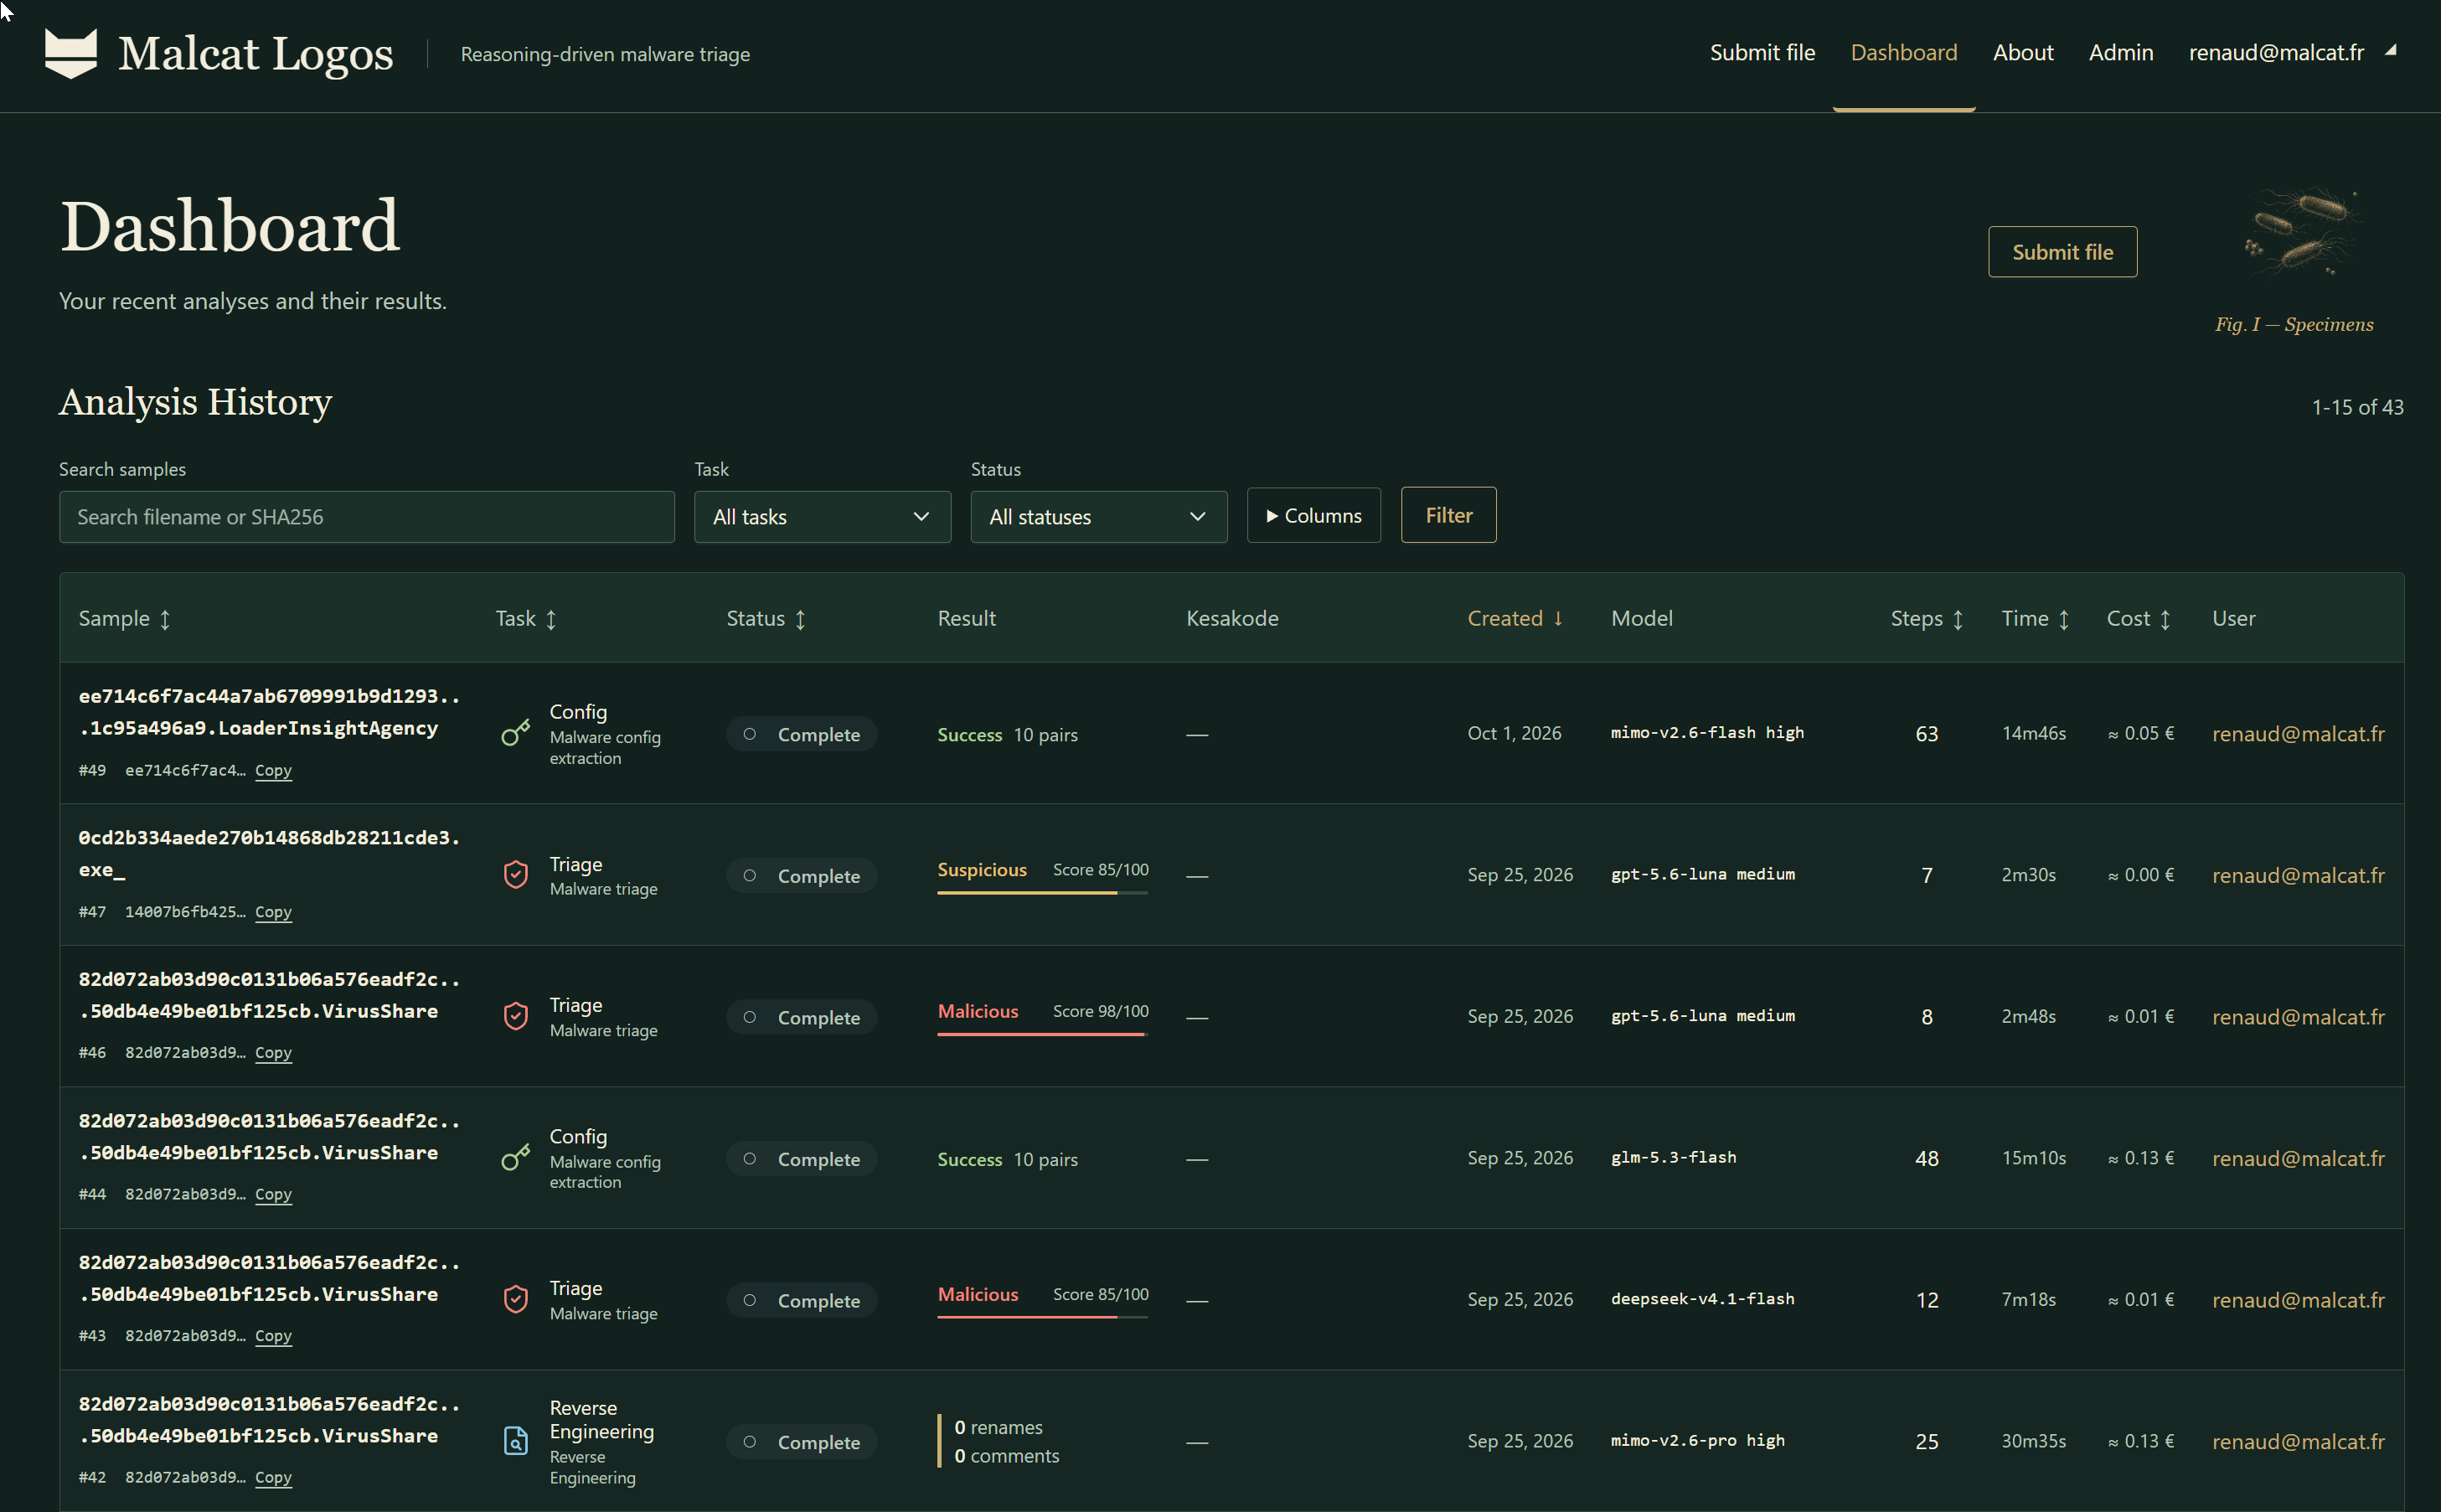
Logos uses Malcat's analysis engine and MCP tools to automate triage, static unpacking and configuration extraction. Choose the task, prompt, model and budget; an analyst reviews the resulting evidence.
Triage and identify
Inspect file structures and code, surface anomalies and detection matches, and use Kesakode evidence to assess a malware family.
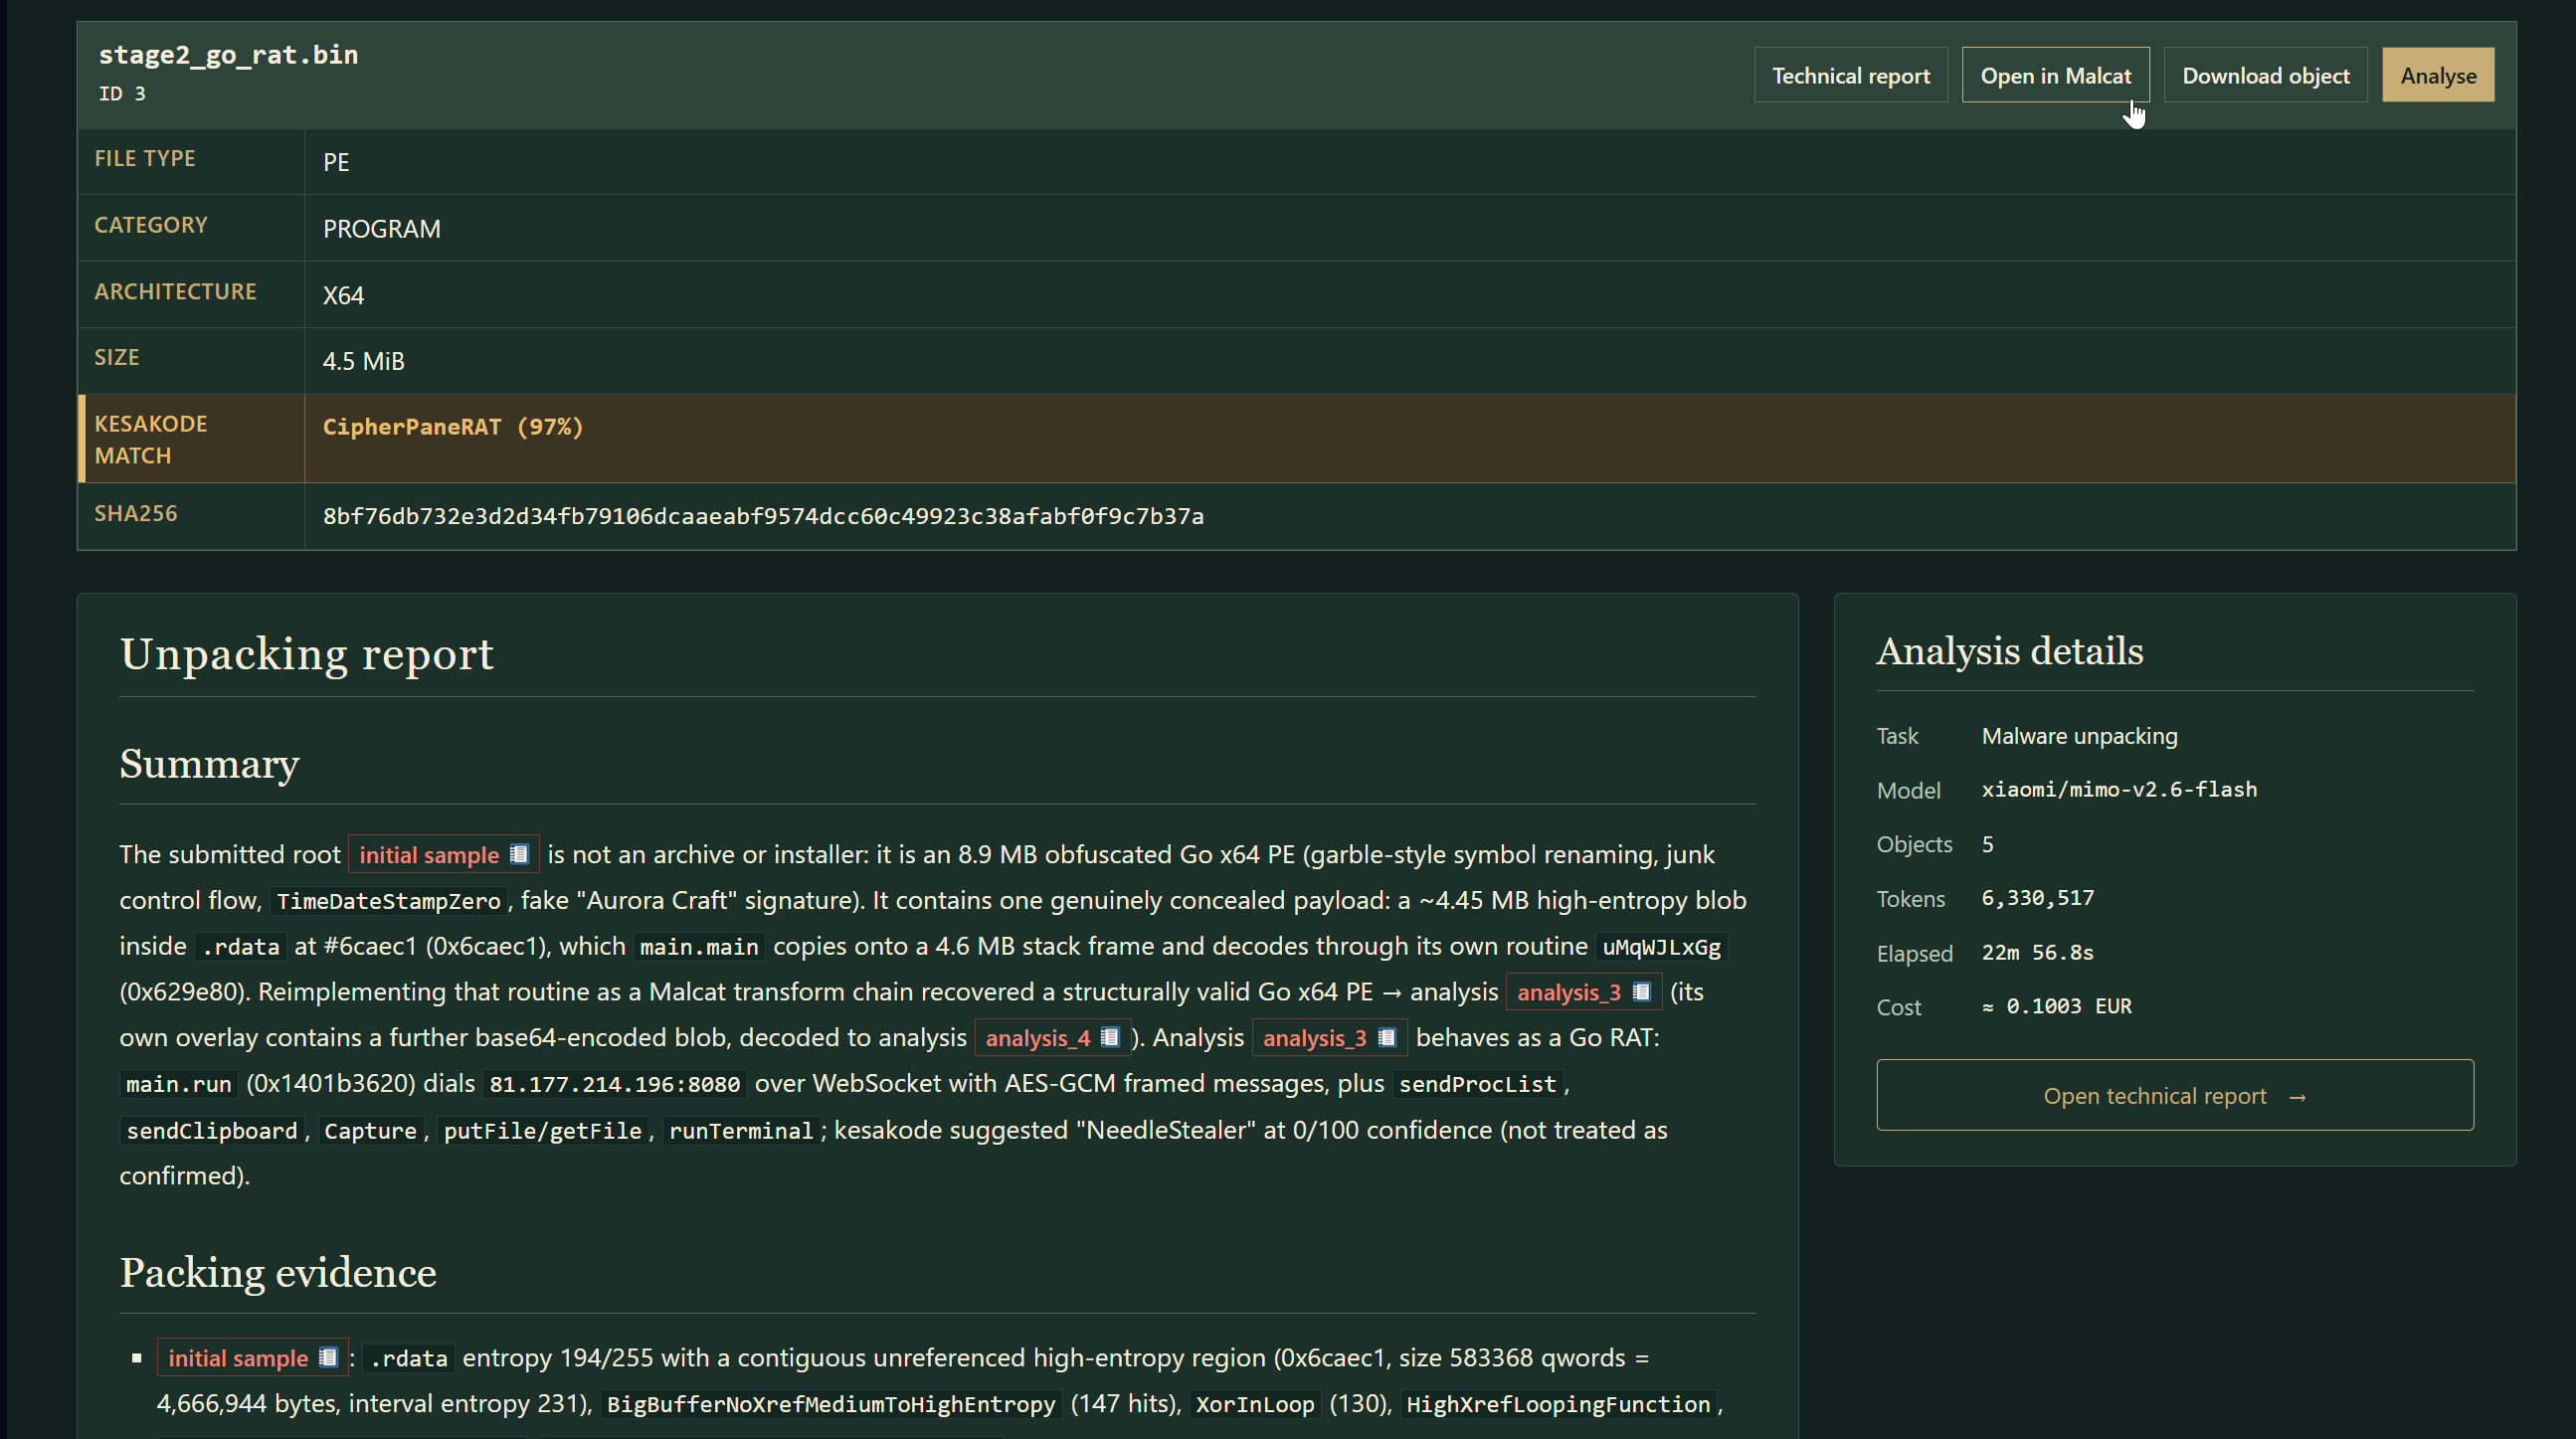
Extract and unpack
Follow archive members and embedded files. Chain Malcat transforms to recover payloads and continue static analysis of the next stage.
Recover configurations
Direct the investigation toward configuration data and indicators, then review the extracted artifacts in the technical analysis.
Deployment and data control
The pipeline runs on-premise. Your model choice determines where prompts and model inputs are processed: a local model or a remote provider through OpenRouter.
Reports and analyst review
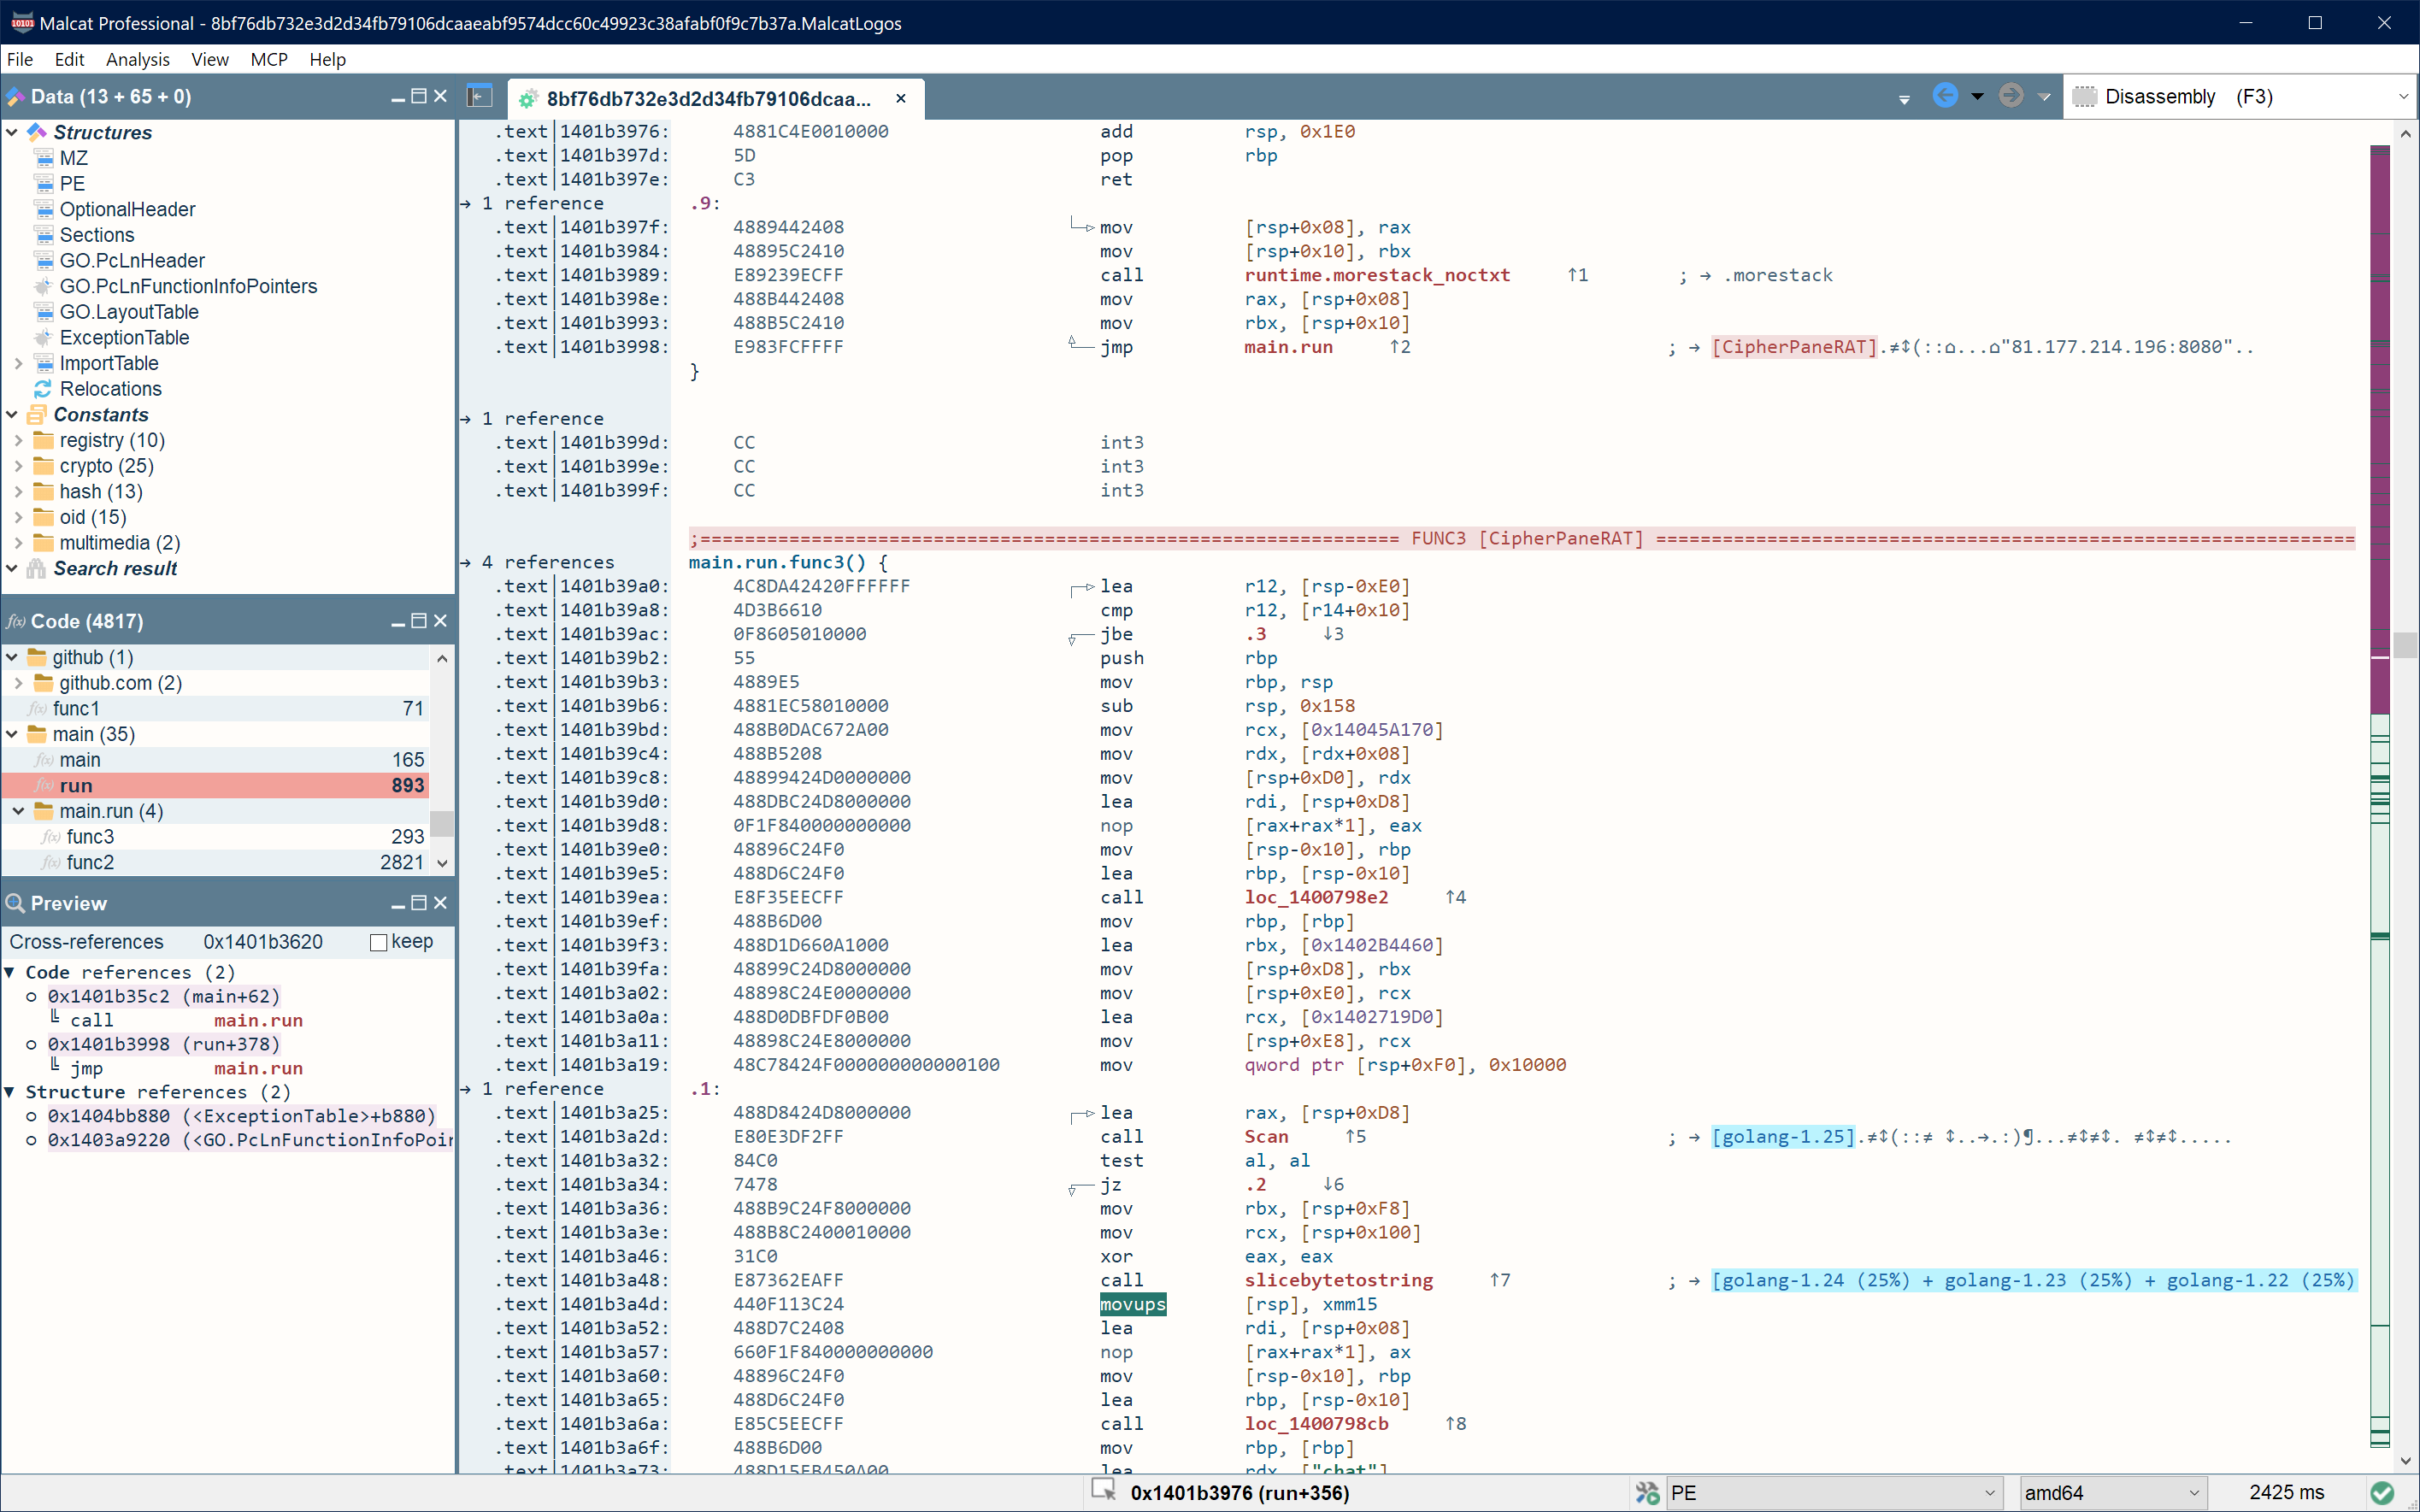
Each investigation includes an AI report and a technical analysis. Use the one-click Desktop handoff to inspect the evidence and unpacked artifacts, add your own analysis and reach a reviewed conclusion.
Included Malcat Pro licenses support that analyst continuation. The exact seat count remains subject to the final Logos offer.
See the Logos application · Request a demonstration · Explore Desktop capabilities